A user agent that says Googlebot proves nothing. How to check a request against Google's published IP lists or a two-way DNS lookup, and how to block impostors in nginx, Apache and Cloudflare without hitting the real crawler.
Posts in category security
This block routes category visitors into the commercial pages and supporting content that complete the search intent.
Audit, hardening, and incident risk reduction.
Hacked site cleanup and closing the entry point.
A free check of your site's public version, results on screen.
Updates checked before release, with a report.
Stability, updates, and post-launch support.
NIS2 and DORA scope mapping, supplier register, incident runbook.
Core Web Vitals, caching, and faster delivery.

A comprehensive WordPress security hardening guide for 2026 covering server configuration, authentication with Passkeys, WAF setup, CSP headers, database protection, headless security, and a 25-point audit checklist.

Passkeys, read-only runtime, edge WAF versus Wordfence, nonce-based CSP, supply chain, logs, and CERT coordination. Hardening is operations, not a plugin checklist.
Passwords are obsolete and perimeter defenses are insufficient. This deep guide outlines the zero-trust architecture, immutable filesystems, and WAF rules for enterprise WordPress in 2026.

Still using "admin"? You are being hacked right now. The definitive guide to securing WordPress authentication: 2FA, Passkeys, Fail2Ban, Cloudflare Turnstile, login monitoring, and incident response procedures.
A user agent that says Googlebot proves nothing. How to check a request against Google's published IP lists or a two-way DNS lookup, and how to block impostors in nginx, Apache and Cloudflare without hitting the real crawler.
After the UpdraftCentral key theft and the tampered Rank Math PRO download in October 2026: how to list every dashboard, app, token and deploy key that can reach your site or shop, revoke what you do not need and rotate the rest.
A visitor clicks Decline and the Network tab still shows Google, YouTube, font and chat requests. How to test it in browser devtools, what usually leaks on Shopify, WooCommerce and custom sites, what advanced consent mode still sends, and how to gate each request.
A buyer or lead hits a Cloudflare block page and leaves. Get the Ray ID and error code, find the event in Security Events, identify the rule (WAF, rate limiting, Bot Fight Mode, Under Attack Mode, country block) and fix it without opening the whole site.
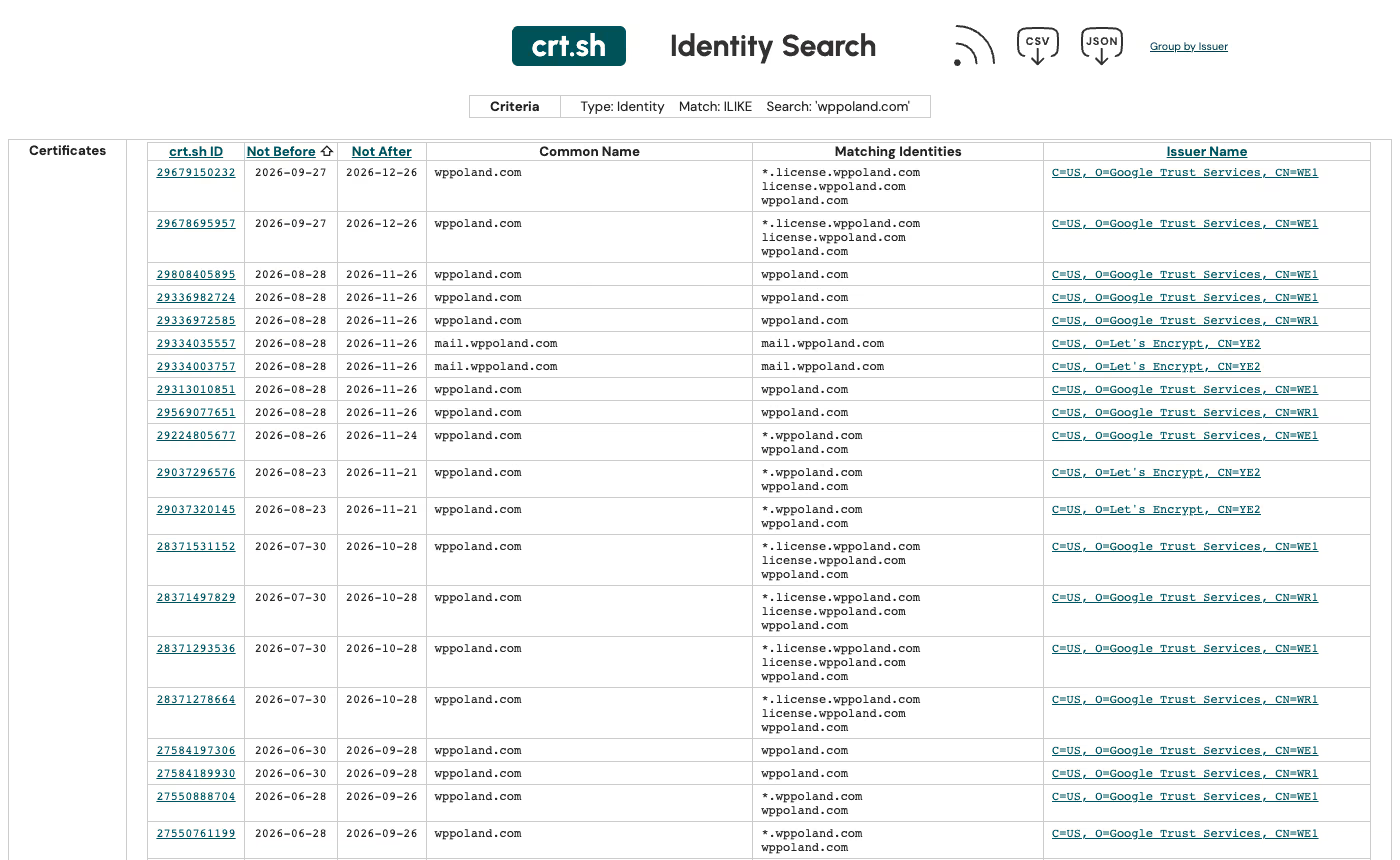
A domain one letter off yours, a copy of your shop, or email that looks like it came from you. How to confirm which it is with RDAP, DNS and certificate logs, lock down your own email with DMARC, warn customers, report the site and dispute the domain.
PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, released on 21 October 2026, fix two critical vulnerabilities in PHP itself (CVE-2026-109618, CVE-2026-109619). How to check the PHP version in WordPress, what to do when your host has not updated the server yet, and which passwords to change after the update.
The open-source intelligence (OSINT) checks a careful buyer, a payment provider and Google Merchant Center run on a new shop, turned into a checklist for an honest shop owner in the UK or Ireland: company details, VAT number, bank account name checks, domain age, photos, reviews and reporting clones.
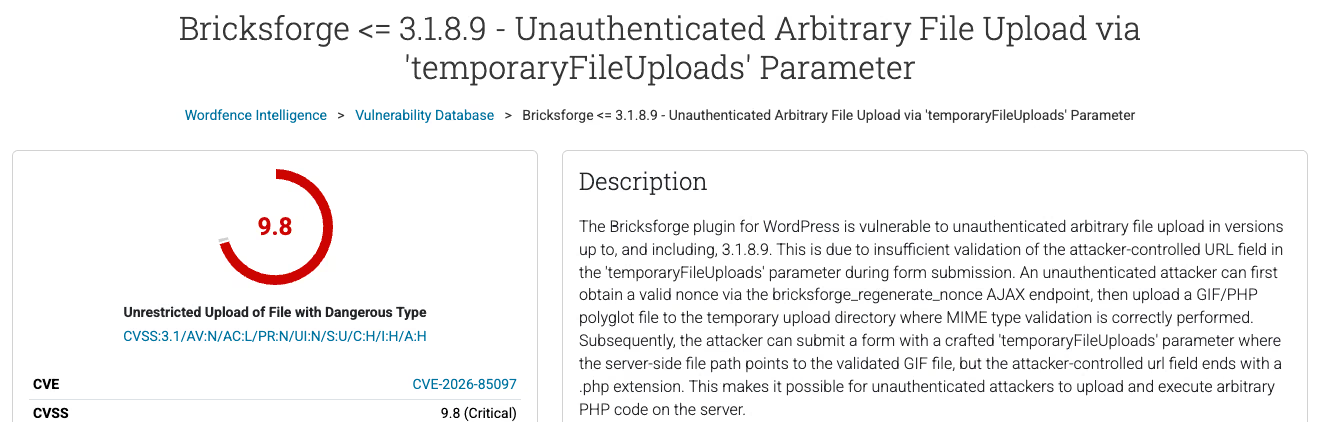
Bricksforge up to 3.1.8.9 lets anyone upload and run PHP through Pro Forms without logging in. Patchstack has seen attacks since 7 October 2026. How to check your version, what to update to and what to look for on the server.
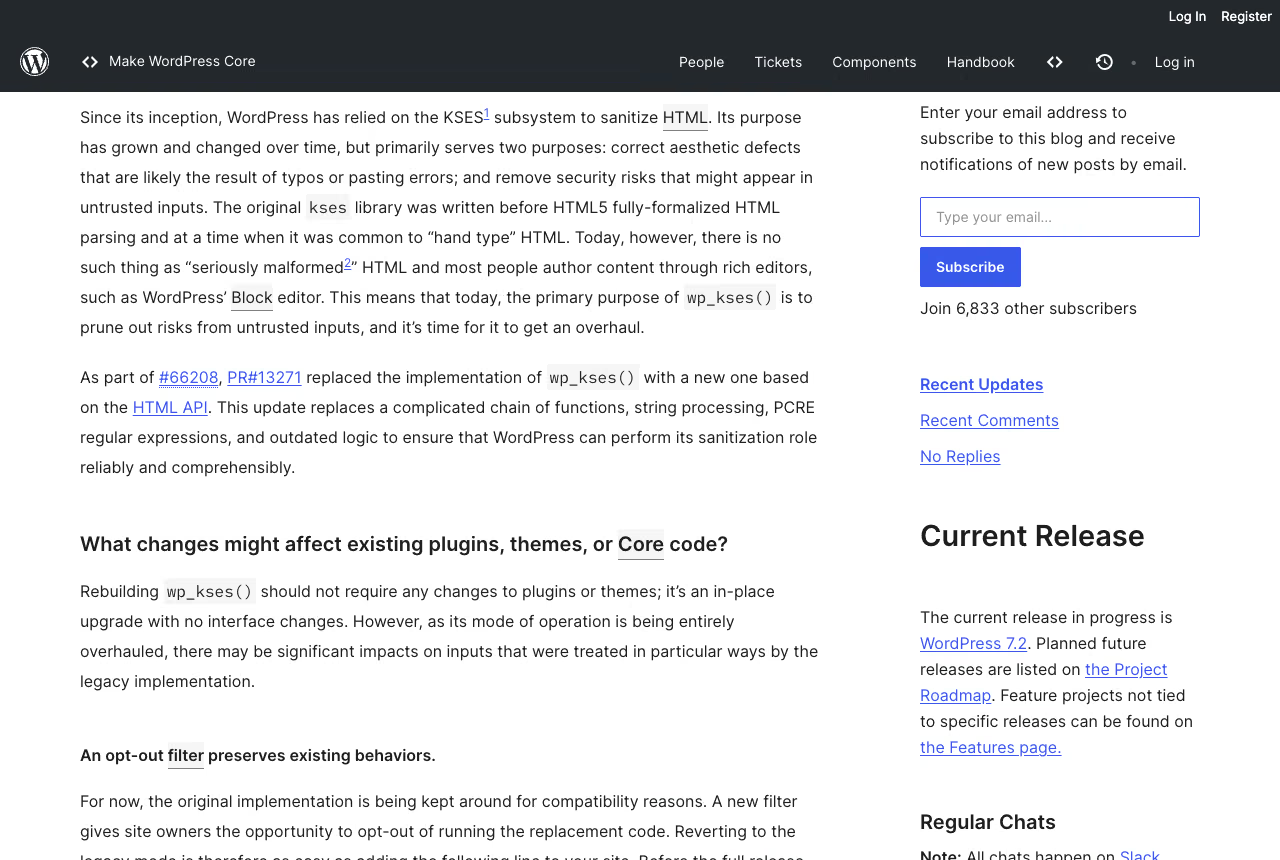
wp_kses() is being rewritten on the HTML API in trunk. What changes for plugin and theme code, how to diff your real content on a trunk build, and what the legacy-parser filter is for.
In 90 days the WordPress security program received 2,004 reports and paid out over $90,000 in bounties. Mary Hubbard is asking more than 30 companies to co-fund it. What it means for a site owner.
An in-depth look at the upcoming WordPress 7.2 release on 8 December 2026, featuring Matt Mullenweg as Release Lead, administrative Sudo Mode, a first-class Secrets API, and interactive editor collaboration.
WP Rocket 3.23.2.1 and earlier fatal on WordPress 7.1: TypeError in Cloudflare.php line 562. GitHub report 6 July, sites down 19 August, fix 3.23.2.2 on 20 August. Update the plugin first.

CVE-2026-65640 needs Author plus Imagick plus Ghostscript. File scanners miss remote JSON. Vibe-coded plugins skip review. Hardening is policy.xml, not another security plugin.
Poland's NIS2 implementation has applied since 3 April 2026. Its definition of a managed service provider covers remote administration, so it describes anyone who maintains someone else's WordPress. What the text says, and what it does not.
We measured the WordPress.org directory. 35,696 of 69,286 plugins have had no update in two years. About 2,100 of them still run on a thousand sites or more each.
WordPress.org holds every plugin release for up to six hours. Patchstack measures the median time to mass exploitation at five hours. The public record does not say whether a security patch is exempt.
The July 2026 wave of the Japanese keyword hack renders only for Googlebot, which is why Wordfence, Sucuri and MalCare report a clean site. How to prove cloaking in one command and clean it in the right order.
An anonymised rescue case: a B2B services site arrived with 38 active plugins, TTFB at 1.47s, and three AI-generated custom plugins on top. How we cut the stack to 21 plugins and brought median TTFB under 0.7s without a rebuild.
Failure patterns in vibe-coded WordPress plugins: missing nonces, unsanitised input, SQL concatenation, absent capability checks, and PHP files without ABSPATH guards. Anonymised audit examples for senior review.
WordPress.org has cut the mandatory update cooldown from 24 hours to six, with work underway to skip it entirely when the Gandalf AI review finds no issues. What changed, and what agencies maintaining B2B sites should do about it.
A real audit of an SME WordPress site: Elementor pinned at 3.11.1, below the fixes for five CVEs listed in NVD, and Contact Form 7 at 5.8 exposed to CVE-2023-6449 (arbitrary file upload). The outdated-plugin pattern, CVE triage, staging updates and WAF limits.
A single week in June 2026 saw the Awesome Motive CDN breach, the ShapedPlugin build pipeline compromise, and a 13-year backdoor campaign exposed. The common thread: the official update channel was the attack vector. What store owners should actually change.
WordPress 7.0 added a Connectors screen that stores AI provider credentials, and some hosts auto-installed AI plugins. Here is the threat model and a hardening checklist.

GuardingWP's inaugural State of WordPress Security 2026 report scanned 424 confirmed WordPress installs across 40-plus verticals. The headline finding is that more than half ship at least one plugin with a known unpatched CVE. Patchstack founder Oliver Sild said WordPress 7.0 will trigger an "absolute rush by hackers to steal API keys." This article reads both as evidence that the plugin economy is the structural problem and NIS2 plus DORA already encode the fix.

Austin Ginder disclosed four WordPress.org plugin backdoors in 30 days, plus an author who ran a hidden update server for five years. What it means for NIS2 and DORA dependency maps.

CRA covers products with digital elements. NIS2 covers entities. DORA covers financial entities. Headless WordPress meets the CRA on the product side and NIS2 or DORA on the client side; for financial entities DORA applies instead of NIS2. I sketch what the joint evidence package looks like in 2026.

Article 28 of Regulation 2022/2554 makes financial entities responsible for the ICT risk of every third-party they touch. I walk through the supplier due-diligence checklist I ship with WordPress engagements for banks and insurers in 2026.

Article 21 of Directive 2022/2555 lists ten risk-management measures every in-scope entity must implement. I map each one to a WordPress agency control, with the evidence file each one requires for audit.

Article 23 of Directive 2022/2555 sets three reporting deadlines: an early warning at 24 hours, a full notification at 72 hours, a final report at one month. What the WordPress agency must produce inside each window.

Article 23 of NIS2 gives 24 hours from awareness to file an early warning with the CSIRT. This playbook lists the WordPress-specific signals that trigger the clock and the template I file when the clock starts.

The NIS2 Directive (2022/2555) was to be transposed into national law by 2024-10-17. The DORA Regulation (2022/2554) applies directly from 2025-01-17. For a WordPress site operator this means specific obligations if the site relates to a regulated entity. We explain it without panic, with references to the texts of the acts.

Thirty-one plugins closed after a Flippa buyer planted a backdoor in the first SVN commit. How to audit plugin ownership, detect compromise, and harden your sites against supply chain attacks.
A comprehensive WordPress security hardening guide for 2026 covering server configuration, authentication with Passkeys, WAF setup, CSP headers, database protection, headless security, and a 25-point audit checklist.

A practical notes covering essential WordPress best practices for security, SEO, and performance using only core features.
Learn how to add passkeys to WordPress with WebAuthn and FIDO2, plus how passkey registration works on iPhone, Android, Windows Hello, and security keys.
Protect your business data by choosing Open Source CMS over closed SaaS platforms in the era of AI. Learn about data ownership, GDPR compliance, and vendor lock-in risks.
Passkeys, read-only runtime, edge WAF versus Wordfence, nonce-based CSP, supply chain, logs, and CERT coordination. Hardening is operations, not a plugin checklist.
Passwords are obsolete and perimeter defenses are insufficient. This deep guide outlines the zero-trust architecture, immutable filesystems, and WAF rules for enterprise WordPress in 2026.

Has your WordPress site been infected with malware? Step-by-step remediation guide for removing backdoors, cloaked spam, and webshells using SSH, WP-CLI, and SQL.

Has your WordPress been hacked? Don't panic. See the complete step-by-step process for removing viruses, backdoors, and malware. SSH, WP-CLI, and SQL methods.
Update crashed your site? Don't panic. See 3 proven ways to rollback WordPress core, plugins, or themes to a previous version.

Comprehensive guide to safely restoring WordPress after failed updates. Learn backup strategies, manual recovery via FTP/phpMyAdmin, plugin-based restoration, and prevention techniques.
Compare the best WordPress plugins in 2026 for security, SEO, cache, backups, and image optimisation, with practical advice on what to install and what to avoid.
A practical 2026 WordPress developer setup: wp-env local stacks, @wordpress/scripts linting, safe debugging, and block tooling without the five-minute-install myth.

Comprehensive WordPress admin guide. Learn how to secure your site without plugins, configure Google Search Console and speed up loading.

A complete WordPress post-installation checklist. 50 steps covering security, performance, SEO and backups. A professional setup from day one.
Stop giving every user Administrator access. Learn how WordPress roles and capabilities really work, and how to design safer permissions.
White-label your WordPress login screen. Change the logo, customize CSS, disable the "Shake" effect, and harden error messages for security.
WordPress displays its version by default, inviting hackers. Learn how to remove the generator tag, asset versions, and implement Security Headers (HSTS, CSP).
Still using "admin"? You are being hacked right now. The definitive guide to securing WordPress authentication: 2FA, Passkeys, Fail2Ban, Cloudflare Turnstile, login monitoring, and incident response procedures.
TimThumb is a security relic. Replace it with core image sizes, srcset, and CDN transforms using native WordPress media handling.